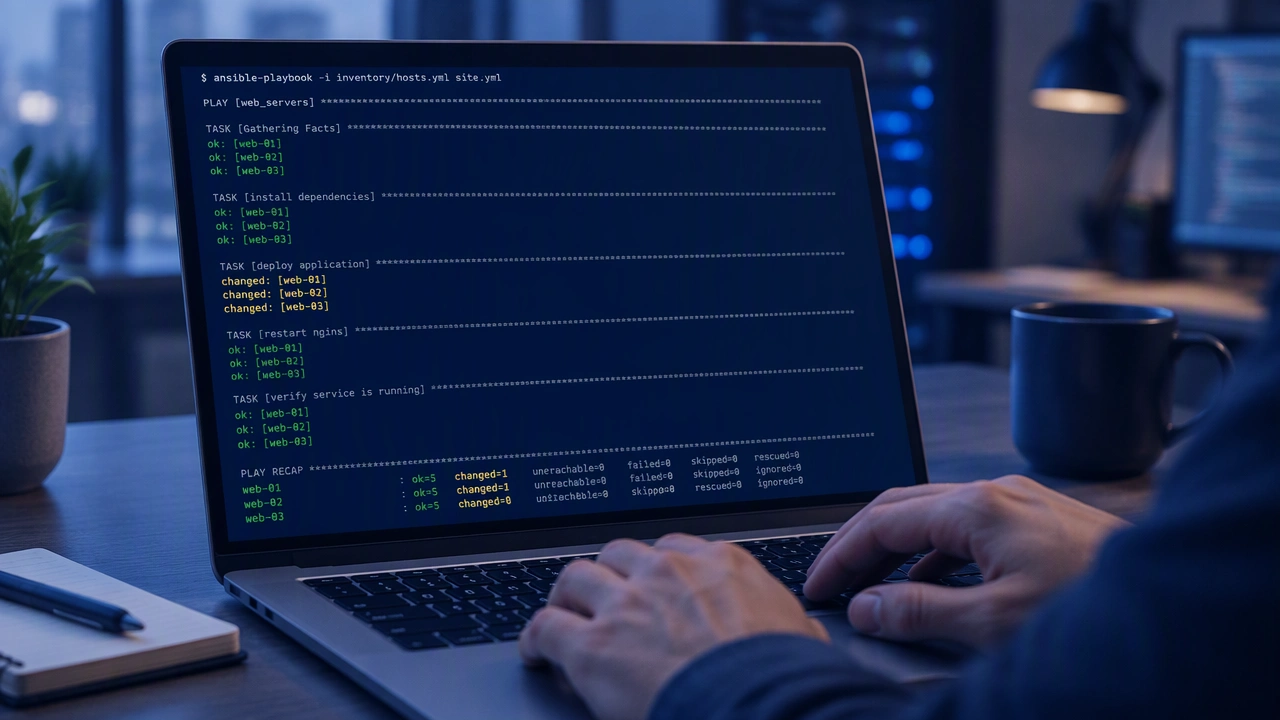
Ansible makes server provisioning repeatable and auditable when you structure your playbooks well. Start with a base role that handles hostname configuration, DNS settings, NTP, SSH hardening, and essential packages. Store playbooks in version control and require peer review before merging changes. Use Ansible Vault to encrypt secrets like API keys and database credentials. Define inventories that separate production, staging, and development environments clearly. Test every role with molecule or a local VM before applying it to production. Use idempotent tasks so playbooks can run multiple times without causing unintended changes. Tag your playbooks so operators can target specific tasks during partial runs. Document every custom module and keep your collection updated.

