How to Perform an Active Directory Password Reset Without Locking Out a User
Password resets are among the most common tasks in IT administration, yet they still create avoidable risk when handled casually. A rushed reset can lock an employee out, interrupt work, or expose credentials to the wrong person. A careful process keeps systems running while protecting accounts from unauthorized access.
Why password resets need a controlled process
A password reset is a privileged action. It can bypass a user’s existing protection if identity checks are weak, and it can trigger account lockouts if old credentials are still cached on a device. The goal is not only to restore access quickly. It is to restore access to the right person, with the smallest possible disruption and a clear record of what happened.
In a typical environment, the process spans Active Directory, a device, sometimes a VPN or cloud service, and the user’s own behavior. Each handoff is a point where mistakes can occur. A repeatable workflow reduces those points and gives the service desk a consistent way to respond.
Before you touch the account
Verify the requester
Confirm the person’s identity through a trusted channel. Use a known phone number, an in-person check, or an existing authenticated support portal rather than details supplied in the request alone. Ask for the username, department, and manager if your procedure requires them. Never accept a password, one-time code, or security answer as proof of identity.
Check the account state
Look at the account status, lockout status, group membership, and recent sign-in events. A locked account, a disabled account, and an expired password can look similar to the user but require different actions. Note the domain controller involved and whether the account is replicated across sites. This context helps you choose the right tool and avoid changing the wrong object.
Choose a safe reset method
Use an approved administrative tool, a supported self-service portal, or your organization’s standard identity provider. Avoid scripts or commands copied from untrusted sources. If you use a script, review it, run it in a controlled context, and make sure it writes only the fields you intend to change.
How to perform an Active Directory password reset without locking out a user
The safest sequence protects identity first, updates the directory second, and clears stale credentials third. Follow these steps in order:
- Confirm the target account. Match the username to the verified requester and check that the account is in the expected organizational unit.
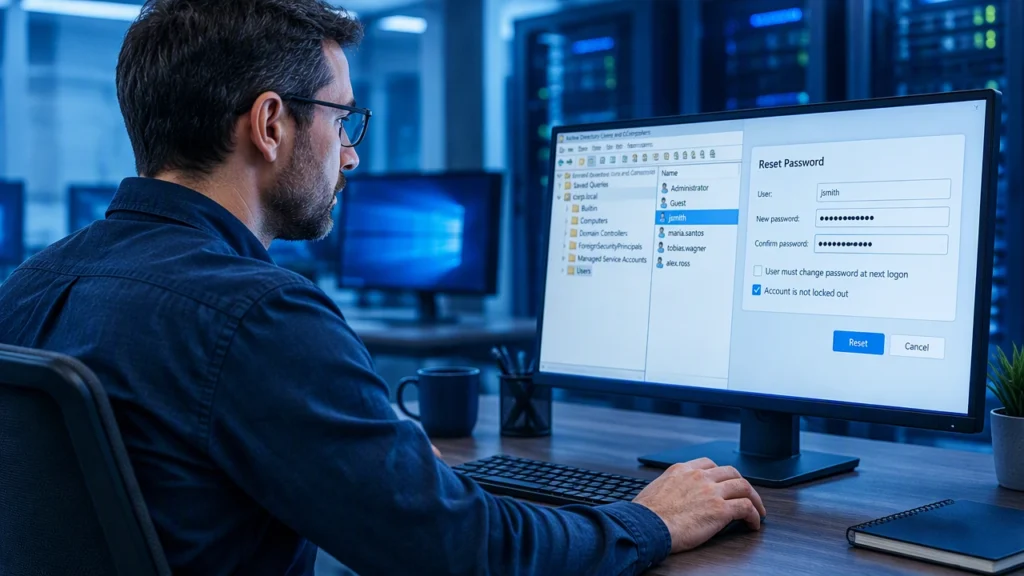
- Reset the password in Active Directory. Set a temporary password that meets your complexity policy, or generate a one-time password through the approved portal. Do not reuse a previous password or a predictable pattern.
- Force the user to change the password at next logon. This keeps the temporary value short-lived and makes the user the owner of the final credential.
- Clear cached credentials where appropriate. On the affected Windows device, remove the old credential from Credential Manager and sign out of cached sessions. For mobile or VPN clients, ask the user to forget the saved network or application credential.
- Unlock the account if needed. If the account is locked, verify the reason before unlocking it. Repeated failed attempts may indicate a stale password on a device, a bad macro, or an ongoing attack.
- Instruct the user to change the password everywhere. Include email clients, remote access, shared applications, and any system that stores the old password. Change it first on the primary device, then reconnect other services.
- Monitor sign-in and lockout events. Watch for a new lockout within the first few minutes. If it returns, investigate the source instead of repeatedly unlocking the account.
Keep communication concise. Tell the user what will happen, when it will happen, and what they must do next. Never send the temporary password in an unencrypted message or leave it on a shared ticket.
Preventing lockouts during the reset
Lockouts usually come from old credentials still being used after the directory password changes. Common sources include saved passwords in Outlook, Teams, mapped drives, scheduled tasks, services, mobile mail, VPN profiles, and scripts. Before the reset, ask where the account is used. After the reset, clear or update those sources in the same session when possible.
Also check the lockout policy. Understand the threshold, observation window, and duration so you can interpret events correctly. If the threshold is low, a few stale retries can lock the account quickly. If the user is in a hybrid environment, allow time for synchronization and avoid changing the password repeatedly while replication is in progress.
When a lockout recurs, trace the event to its source. Review the domain controller event logs for the lockout source and identify the workstation or service that submitted the failed attempts. Fix the source, then unlock the account. Unlocking without correcting the cause simply repeats the interruption.
Protecting the account after the reset
Use a temporary password that is unique, random, and never shared in advance. Require the user to set the final password from a trusted device. Confirm that multifactor authentication still works and that recovery methods are current. If the reset follows a suspected compromise, review recent sign-ins, delegated permissions, mailbox rules, and connected applications.
Record the action in the ticket: who verified the requester, which account was changed, when the password was reset, whether the account was unlocked, and which devices were updated. The record supports audits and helps the next administrator avoid repeating work.
Reducing service interruptions
Plan resets during a quiet period when the user can complete the change without a deadline. Provide a clear fallback if the user cannot sign in, such as a verified support channel or an in-person identity check. Keep a short checklist at the service desk so every technician follows the same order.
For high-impact accounts, coordinate with the application owner and confirm that service accounts are not accidentally included. Test the reset path with a nonproduction account when you change tools or policies. Small rehearsals expose missing steps before they affect production.
A practical standard for every reset
Treat every password reset as a security operation with a service objective. Verify identity, understand the account state, use approved tools, clear stale credentials, and watch for immediate relockouts. Document the result and close the loop with the user.
When the process is routine, teams move faster with fewer surprises. Users regain access, accounts stay protected, and the organization avoids the cascading interruptions that come from repeated lockouts, confused handoffs, and untracked changes.